Authentication
Use a dedicated operational bearer credential. Do not reuse a browser login or core API token.
Verified behavior
- Credential is issued to an active company employee
- Token holds explicit scopes and expiry
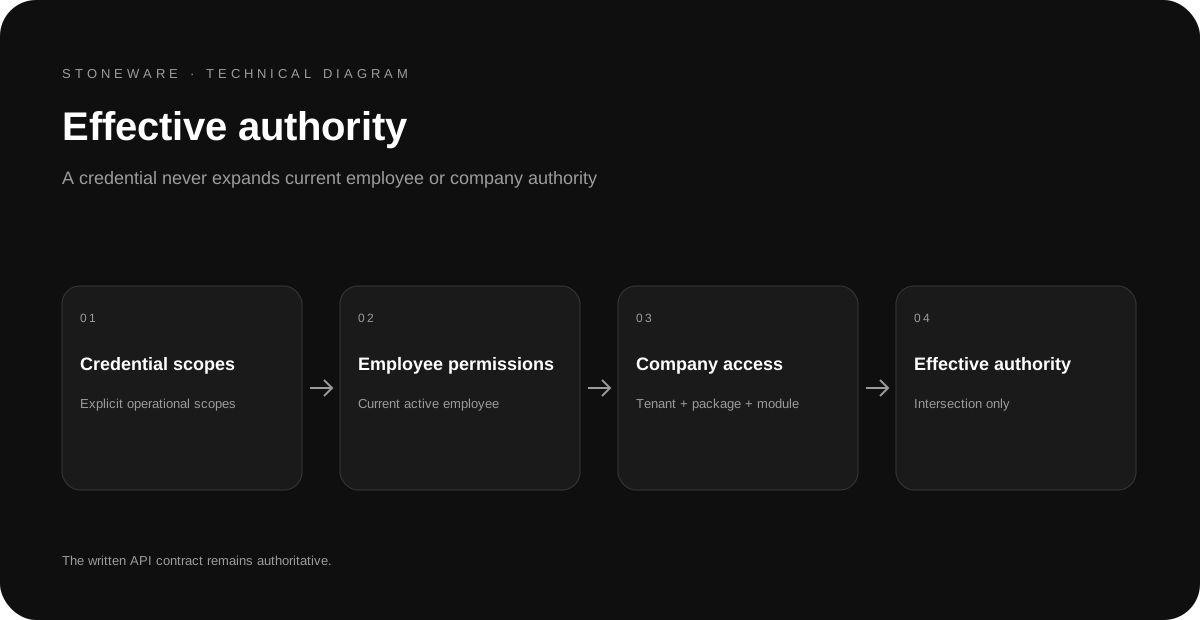
- Effective authority = token scope ∩ current employee permission
- Company/package/module access is rechecked on every request
- Never embed the token in browser JavaScript or a distributed mobile app
cURL
curl 'https://your-company.example/api/slab/v1/operations/capabilities' \
  -H 'Authorization: Bearer YOUR_OPERATIONAL_TOKEN' \
  -H 'Accept: application/json'
Important
All example hostnames, IDs and tokens are placeholders. Test against staging first. The installed runtime services and exact OpenAPI contract remain authoritative for state transitions, nested schemas and additional permission checks.