Integrate the physical operation.
Server-to-server access to stone inventory, purchasing, receiving, reservations, warehouse and fulfilment — with company, employee, permission and retry controls intact.
/api/slab/v1/operations/slabs?warehouse_id=1&per_page=30Authorization: Bearer slabop_…
Accept: application/json
200 OK
{
"data": [ … ],
"meta": {
"per_page": 30,
"has_more": true,
"next_after_id": 348
}
}Start from the business object you are integrating.
The public operational contract is organised around canonical Stoneware resources and workflow actions.
Exact stone & locations
Slabs, remnants, materials, warehouses, locations, movements and related inventory context.
Open Slabs reference →PROCUREMENTInbound operation
Suppliers, purchase orders, shipments, containers, receipts, exceptions and landed cost.
Open PO reference →COMMITMENTReservation & allocation
Projects, selections, reservations, quote links and allocations around exact physical stock.
Open Reservations reference →FULFILMENTPick, dispatch & return
Fulfilments, proof, dispatch context and returns using the same authoritative state.
Open Fulfilments reference →Understand the boundary before you write integration code.
These diagrams summarize the verified operational contract; the endpoint reference and workflow rules remain authoritative.
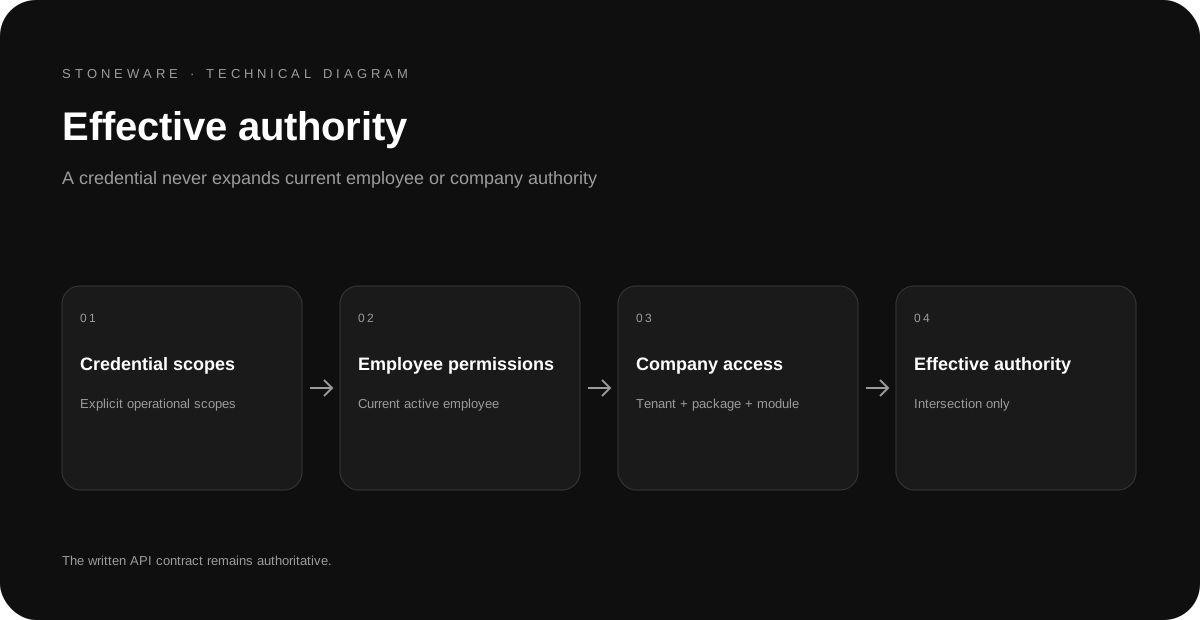 Authority intersection
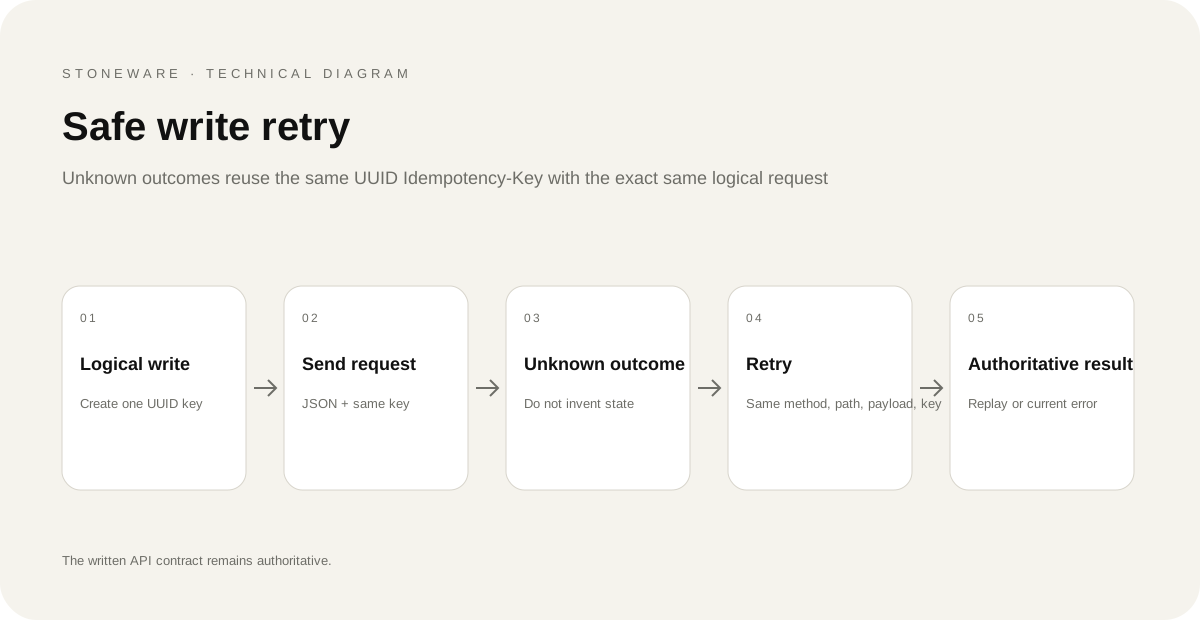 Safe retries
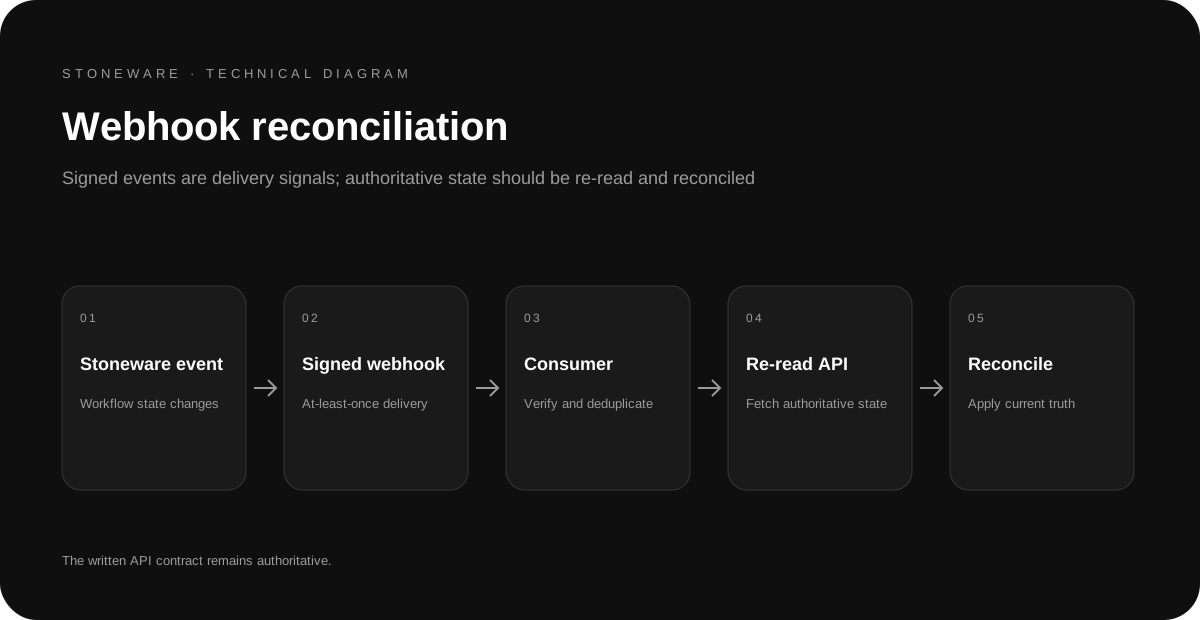 Webhook reconciliation
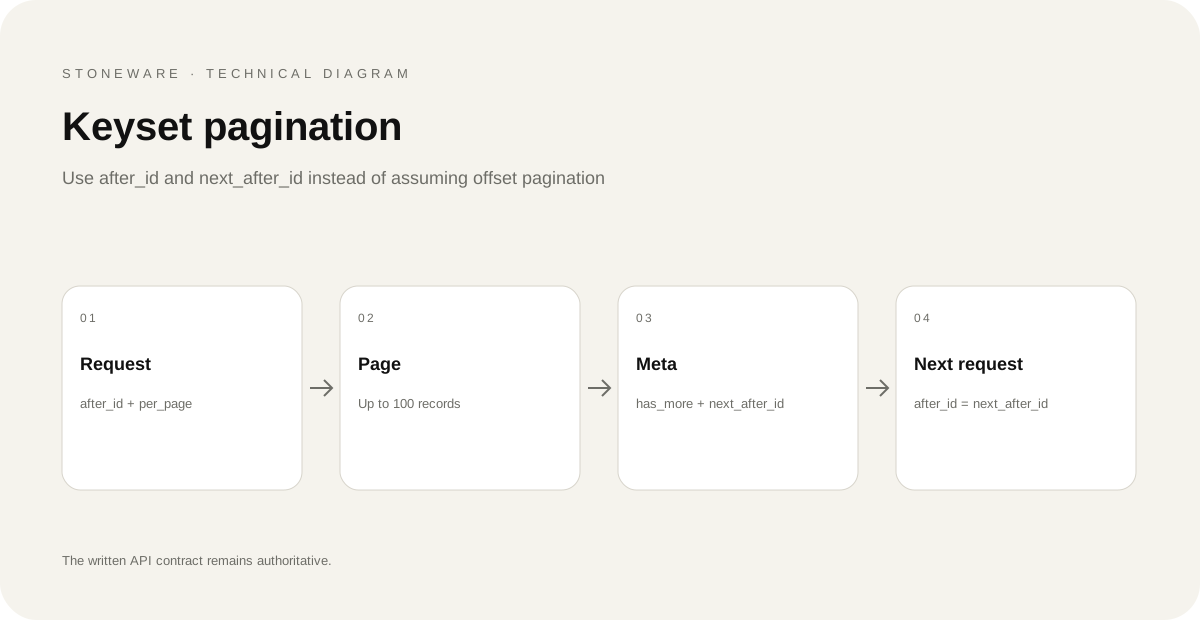 Keyset pagination
Authenticate
Company + employee scoped operational credentials.
02Retry safely
UUID idempotency keys and replay protection on every write.
03Reference
41 reads and 79 mutations grouped by operational domain.
04Code examples
Verified read patterns in cURL, JavaScript, PHP, Python and C#.
05Workflow recipes
Use the API in the same operational sequence as Stoneware.
06Errors & limits
Design for permission failures, validation, conflicts and retry limits.
Build a trusted service around Stoneware — not a second workflow engine.
The operational API is designed for server-to-server integration that respects current company access, employee permissions and authoritative Stoneware state.
Build against the workflow boundary.
Keep integrations company-scoped, permission-aware and safe to retry.
This operational API does not create customer, invoice, accounting, ARI or Supplier Finance & FX records unless an endpoint is explicitly present in the verified contract. Those areas remain owned by their authoritative Stoneware workflows, and this portal does not publish invented endpoints for them.
Web v3 documents more product capability than the current public operational contract exposes.
ARI and Supplier Finance & FX are documented as Stoneware application capabilities. Do not infer a public API from a product page: only endpoints listed in the verified reference are supported.